What is a DDoS attack: how it works and the main types
What a DDoS attack is, how botnets work, the main types of attack and what to do if your website comes under attack. Explained simply.
One morning your website simply stops opening. The hosting is running, nobody has touched anything, yet the pages load forever or return an error. An hour later everything is back to normal, and that evening the same thing happens again. Cases like this are often caused by a DDoS attack: an attempt to bury a website under so many requests that it can no longer serve its real visitors.
In this article you'll learn what a DDoS attack is, how it works, what types of attacks there are, why anyone would attack your website in particular and what to do if it happens. No technical jargon where it isn't needed, and no unnecessary scaremongering.
In short
- A DDoS attack floods a website or server with a huge number of requests from thousands of devices at once, until it stops responding.
- The devices are usually infected computers, routers and cameras whose owners have no idea they're taking part.
- There are three main types of attack: volumetric attacks, protocol attacks and attacks aimed at the website itself.
- DDoS isn't hacking: no data is stolen, but the service goes down.
- A high-volume attack can't be stopped on the server alone. Filtering has to happen earlier, in the provider's network.
What is a DDoS attack
DDoS stands for distributed denial of service. Its goal isn't to steal anything but to make a website, server or network unavailable to the people who actually want to use it.
The easiest way to picture it is with an example. A small shop has one door and one cashier. If a thousand people stand at the door, walk in, ask a question and walk out without buying anything, the real customers simply can't get in. The shop hasn't been robbed, but it isn't working for anyone. That's exactly what a DDoS attack does to your website.
The difference between DoS and DDoS lies in the word "distributed". In an ordinary DoS attack, the requests come from a single source, which is easy to block. In a DDoS attack, they come from thousands or even millions of different addresses around the world. That makes the attack much harder to stop: there's no single culprit to cut off.
How a DDoS attack works: botnets
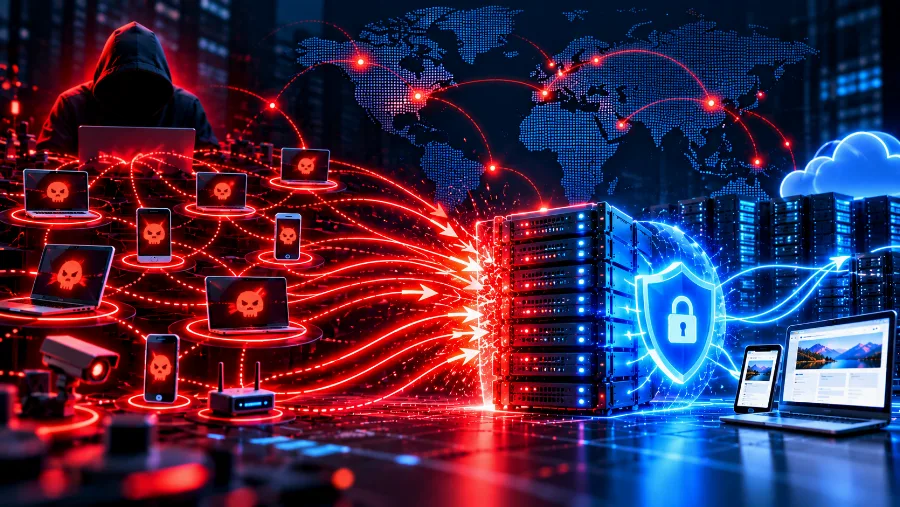
Most DDoS attacks are carried out through a botnet, a network of devices infected with malicious software. These can be ordinary home computers, old routers, security cameras, smart TVs and all kinds of other internet-connected devices with poor protection.
The owners of these devices usually have no idea they're taking part in an attack. The device seems to work normally, but at some point it receives a command from the server that controls the botnet and starts sending requests to the target. When tens of thousands of devices do this at the same time, even a powerful server can't keep up.
That's why protecting your own devices is a shared responsibility too. Changing the factory passwords on your router and cameras and keeping them updated stops them from becoming part of the next attack on someone else.
Types of DDoS attacks
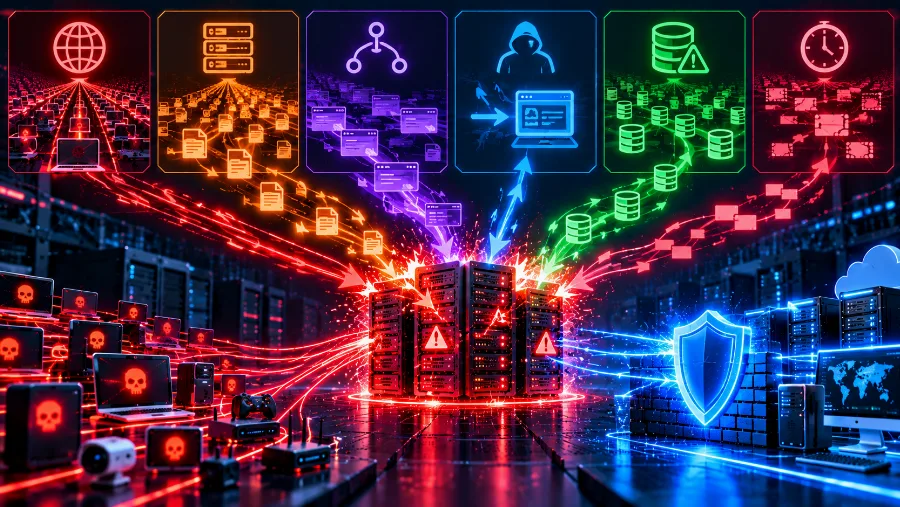
Attacks differ in which part of the path to the website they overload. This matters, because each type is stopped in a different way.
| Type of attack | What it overloads | Example | How it's stopped |
|---|---|---|---|
| Volumetric | The internet connection to the server | UDP flood, DNS amplification | Filtering in the provider's network, before the traffic reaches the server |
| Protocol | Network equipment and the server's connection resources | SYN flood | Specialised network filters and correct server settings |
| Application layer (L7) | The website itself: PHP, the database, search | Mass HTTP requests to heavy pages | Behaviour analysis, request rate limits and caching |
Volumetric attacks are the bluntest. Their only aim is to fill up the internet connection, the way a flood blocks a road. They're measured in gigabits per second, and the largest attacks on record reach terabits. On its own, the server is helpless against them, because the connection is full before the traffic even gets there.
Protocol attacks exploit the way devices set up connections with each other. The attacker opens thousands of connections but never completes them, and the server runs out of capacity for pending connections.
Application-layer attacks are the most cunning. They look like normal visits but target the heaviest parts of the website: search, filters, the cart or the login page. They don't need much volume, because every request makes the server work hard. That's also why they're the hardest to recognise.
DNS amplification: when DNS becomes a weapon
One of the best-known types of volumetric attack abuses DNS, the system that translates website names into IP addresses. If you'd like to understand how it works in more detail, see the article on what DNS is.
The idea is simple. Some DNS servers on the internet are misconfigured and answer anyone who asks them. Attackers send them short questions but forge the sender's address so that it's the victim's address. The answer is many times larger than the question and goes not to the attacker but to the target. A small effort on one side turns into a huge flow of traffic on the other.
That's why hosting and internet providers make sure their servers don't answer outside requests and can't be used in this way.
Why would anyone attack your website
Many owners of small websites believe DDoS attacks only affect banks and large companies. In reality, attacks can be ordered for relatively small sums, and the reasons vary widely:
- Unfair competition. An online shop that's down on the day of a sale loses customers to someone else.
- Extortion. The attacker takes the site down briefly and demands payment not to do it again.
- Distraction. An attack is sometimes used as cover while another kind of break-in is attempted.
- Ideology. Websites of institutions, media and organisations become targets because of a position they've taken.
- Games and personal disputes. Game servers and streamers are frequent targets of disgruntled players.
Sometimes a website goes down with no attack at all: a post that suddenly goes viral can bring more visitors than the hosting plan was designed to handle. The effect is similar, but the cause is completely different.
What the logs show during an attack
If you have access to your hosting statistics or server logs, an attack usually leaves telltale traces:
- a sharp spike in traffic that doesn't match a campaign, a post or a seasonal peak;
- thousands of requests from different IP addresses, often from countries the site normally gets no visitors from;
- many requests to the same page or address, such as the search or the login form;
- unusual or empty details about the browser the requests come from;
- processor and memory usage maxed out, with no real increase in orders or enquiries.
None of these signs is proof on its own, but when several appear at once, there's a good chance you're dealing with an attack.
What to do during a DDoS attack
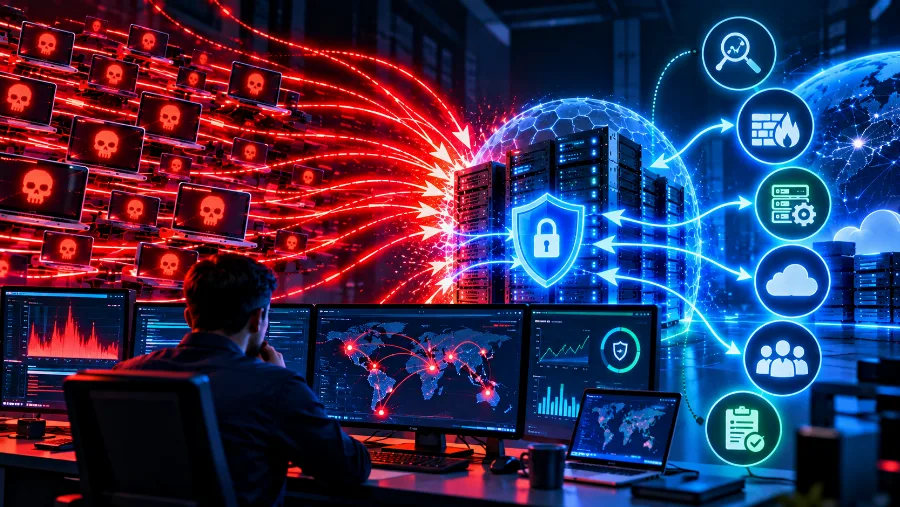
The first rule is not to act in a hurry. Here's a sensible order of steps:
- Contact your host straight away. They can see the traffic at network level and can tell whether it's an attack and what's being filtered right now.
- Don't restart the server again and again. It doesn't stop the attack; it only makes the downtime longer.
- Write down what's happening. Times, symptoms, error messages and screenshots will help your host and, if needed, the authorities.
- Don't pay a ransom. If you receive a demand for money, paying guarantees nothing and only marks you as an easy target.
- Check your other services. Email, applications and other websites on the same server may also be affected.
- Think about next time. Once the attack has passed, look at what was vulnerable and what could be improved.
A DDoS attack isn't hacking
This is one of the most common misunderstandings. In a DDoS attack, nobody gets into your website, reads your database or steals passwords. The attack takes the service down but doesn't break into it. Once the traffic subsides, the website works exactly as before, with all its data intact.
That doesn't make DDoS harmless. An hour of downtime at the wrong moment can cost more than a month's hosting budget. And, as mentioned, an attack is sometimes used as cover for a break-in attempt. So after any attack it's worth checking your site's security too: are the system and plugins up to date, and are there any administrators you don't recognise?
How a DDoS attack is stopped
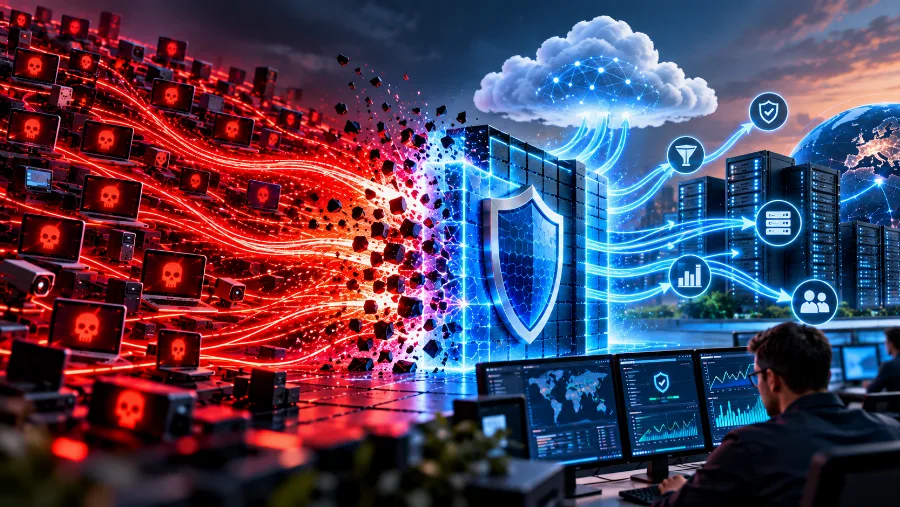
The key principle is that an attack must be stopped as far away from the server as possible. If the huge traffic reaches it, the connection is already full and no settings on the server itself will help. That's why effective protection works on several levels:
- In the provider's network. Specialised equipment recognises the fake traffic and filters it out before it reaches the server.
- Request limits. A single address can't send an unlimited number of requests in a short time.
- Caching. Ready-made copies of pages are returned quickly, without loading PHP and the database.
- Monitoring. Unusual behaviour is spotted in time, not once the site has already gone down.
That's why a WordPress security plugin, however good, won't save you from a volumetric attack. It works inside the website, while the traffic jams the road long before that. We explain exactly how network protection works, layer by layer, and what remains your responsibility on the DDoS protection page.
DDoS and VPS: who is responsible for protection
With shared hosting, network protection is entirely the provider's job. With a VPS, things are a little different. Filtering large attacks still happens in the provider's network, because that's the only place it's possible. But the settings on the server itself, such as the firewall, connection limits and caching, are your responsibility if the VPS isn't managed.
So if your project is a frequent target of attacks, check what network protection is included when you choose a VPS server. And if you're still wondering whether a VPS is the right choice for you, start with the article on what a VPS is.
How to prepare your website in advance
The best time to think about DDoS is before an attack, not during one. A few simple steps make a big difference when the day comes:
- Turn on website monitoring. A free service that checks your site every minute and messages you when there's a problem will tell you about an attack straight away, not when a customer complains.
- Turn on caching. The more pages are served as ready-made copies, the less work the server has to do and the longer it holds up under load.
- Lighten your heavy pages. Search, filters and forms are the favourite targets of application-layer attacks. Limit how often a single visitor can use them.
- Keep your server's real address private. If your site goes through a protection service or a CDN, don't publish the server's direct IP address in subdomain DNS records or in emails. Otherwise attackers can bypass the protection.
- Have a plan and contacts. Write down in advance how to reach your host's support team and who on your team does what if there's a problem. In a stressful moment, you won't waste time looking for a phone number.
- Check what your hosting includes. Ask whether there's network DDoS protection, whether it's included in the price and what happens to your site in a very large attack.
None of these steps requires a big budget, but together they turn an attack from a disaster into an unpleasant but short episode.
Myths about DDoS attacks
- "Only big companies get attacked." Small websites are often an easier target, because they rarely have protection and attacking them costs little.
- "More resources solve the problem." A more powerful server holds out a little longer, but it doesn't help against a volumetric attack. The connection fills up regardless of the processor.
- "My security plugin protects me." It protects against break-ins, but not against traffic that clogs the connection before it reaches the site.
- "The attack will delete my website." DDoS doesn't delete or change any data. It only makes the website temporarily unavailable.
Frequently asked questions
What does DDoS stand for?
DDoS stands for distributed denial of service. "Distributed" means the requests come from many different devices at the same time.
Are DDoS attacks legal?
No. In Bulgaria, as in almost every country, deliberately disrupting someone else's information system is a crime. This applies to ordering an attack as well, not just to carrying it out.
How long does a DDoS attack last?
Most attacks last from a few minutes to a few hours. Some come back in waves over several days, especially when the goal is extortion or competition.
Can my home internet connection be attacked?
Yes, if someone knows your public IP address. This mostly happens to gamers and streamers. If your address is dynamic, restarting your router often changes it and the attack stops. For repeated attacks or a static address, contact your internet provider.
Does a DDoS attack affect Google rankings?
A short attack has no effect. If the site is unavailable for a long time or often, the search engine may fail to crawl it and temporarily rank it lower. Once the site is stable again, rankings usually recover.
Conclusion
A DDoS attack is an attempt to bury a website, not to break into it. It doesn't steal data, but it can stop sales, enquiries and customer trust at the worst possible moment. The good news is that there's effective protection against it. The key is for it to work before the traffic reaches the server, not after. Now that you know how attacks work, you can judge whether your website is protected and what to do if one day it does come under attack.
Want your website to stay online even during an attack? See how network protection stops fake traffic before it reaches the server.